


Information Security
Information Security Policy
We regard all of our own information assets as one of our management resources. Through the proper protection and effective use of our information assets, we pursue healthy maintenance and development of our business.
Action Guidelines
- We establish rules that clearly define the system and responsibilities for the protection and management of all the information assets including the information we keep for our customers, the know-how and intellectual properties owned by our group, and personal information.
- We comply with laws, ordinances, and regulations regarding information security.
- We educate all executives and employees who handle information assets about the importance of information security, and about specific items to be observed.
- We continuously update the information infrastructure for the maintenance and improvement of the confidentiality, integrity, and availability of all the information assets.
- We promote measures to prevent accidents in order to address the risks of information leakage associated with the continuous advancement and sophistication of information technology. Should an accident occur, we will strive to minimize the damage and take preventive measures against recurrence.
- We establish requirements necessary for the maintenance and improvement of our information security level for business partners, including suppliers, who handle our group's information assets, and promote appropriate management.
Basic Philosophy
As the importance of information security increases, it is necessary for management and frontline staff to work together to enhance the effectiveness of information security management and reduce security risks to our group's information assets. In particular, the digital sector is facing increasing threats from cyberattacks, including those using AI. We have always separated digital-related aspects of information security as IT security and have established a system to respond quickly. Furthermore, we are committed to the proper protection of various confidential and personal information, including information entrusted to us by external parties.
Promotion System
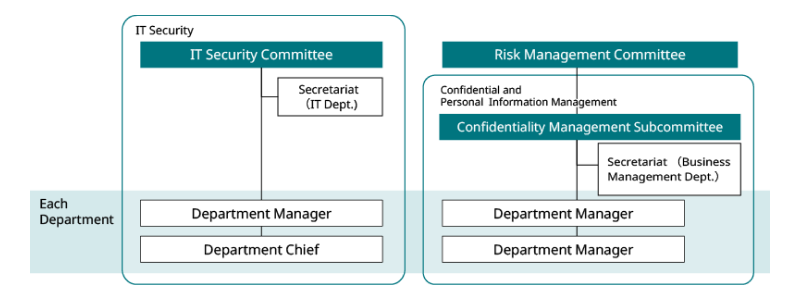
Our group has established promotion systems for each area, namely IT security and confidential/personal information management, and is working together to strengthen information security.
Regarding IT security, we have established an IT Security Committee chaired by the Executive Officer in charge of Global Strategy (holding regular meetings twice a year and extraordinary meetings as needed) to review the company-wide IT security activities and promote appropriate countermeasures. Important decisions made by the IT Security Committee are reported to the Board of Directors through the Management Meeting. In fiscal year 2025, the IT Security Committee held two meetings to report and discuss incidents, activities to strengthen IT security, and ISMS activities. We also held a global meeting to maintain and strengthen the security system across the entire group.
On the other hand, regarding the management of confidential and personal information, a Confidentiality Management Subcommittee has been established under the Risk Management Committee (holding regular meetings once a year and extraordinary meetings as needed), with the Executive Officer in charge of Business Management serving as the subcommittee chairman, to promote the reduction of risks related to the management of confidential and personal information. In fiscal year 2025, the Confidentiality Management Subcommittee held one meeting, where incident reports and explanations regarding revisions to the privacy policy were conducted.
Furthermore, within each department, a person in charge and a person responsible for each area of IT security and confidential/personal information management are in charge of leading information security activities.
Information Security Management System
In order to continuously address information security risks that threaten companies and organizations, we have set information security as a primary management priority and are proceeding with the construction of an information security management system equivalent to ISO 27001.
In recent years, the digital transformation of business operations has progressed, and the range of risks that need to be considered has expanded, including the use of generational AI. Therefore, we are continuously working to improve our information security management system by including these new risks in the evaluation criteria. We conduct annual audits of IT security and IT systems at all locations and promptly correct any deficiencies that are identified.
Furthermore, at the request of some automobile manufacturers, we have obtained TISAX certification, which is an information security assessment standard for the automotive industry's supply chain.
Responding to Information Security Incidents
To respond to information security incidents, we have established a CSIRT (Computer Security Incident Response Team).
When an incident occurs, the CSIRT (Computer Security Incident Response Team) promptly organizes and verifies the facts, determines the severity of the incident, and then takes action. Furthermore, they implement knowledge accumulation and sharing as a preventative measure against recurrence.
We focus not only on responding to incidents after they occur, but also on proactive prevention, striving to improve our security level and maturity from both a pre- and post-incident perspective.
Information security education and awareness
Improving employees' information security awareness is essential to preventing information security incidents, and we conduct education and awareness campaigns through various training programs and educational tools.
- Education on information security policies and rules
- We conduct annual training sessions for employees of our company and domestic group companies on information security policies, information security management systems (ISMS), and IT security-related regulations, and we also check their level of understanding.
- Information Security Awareness Training
- Every year, we conduct training for our employees, including executives, continuing employees, and temporary staff of our domestic group companies, to help them understand the types of information security threats, the impact they cause, and the countermeasures and mindset required to deal with them. In fiscal year 2025, we conducted this training three times.
- CSIRT communication
- The CSIRT publishes a monthly newsletter, "CSIRT Communication," to inform employees of the latest information on information security and to raise awareness. When a high-priority alert is needed, they issue an urgent version containing specific precautions, working to prevent incidents from occurring in the first place.
Confidential management
The Confidentiality Management Subcommittee conducts an annual inspection of the company-wide implementation of confidentiality management based on the established confidentiality management rules. The Confidentiality Management Subcommittee Secretariat verifies the validity of the self-inspection results from each department and works to strengthen the checking function. In fiscal year 2025, in order to promote thorough information management through education and awareness activities for employees, in addition to regular training, we conducted awareness campaigns regarding confidentiality management.
In addition to confidential information handled internally, we have established rules to prevent the leakage of confidential information taken outside the company, such as procedures for using mobile computers and cloud services, and we verify compliance with these rules.
Protection of personal information
In response to the global trend towards strengthening personal data protection, such as the European General Data Protection Regulation (GDPR) and Japan's Personal Information Protection Act, each company within our group has established regulations to thoroughly protect, manage, and handle the personal information of our customers and employees. In fiscal year 2025, we revised our privacy policy, regulations, and guidelines, incorporating changes such as a review of the purpose of use and the utilization of pseudonymized information.
Our policy regarding the handling of personal information (privacy policy) is outlined below.